Context and safety notes
This guide is aimed at merchants and technical administrators running PrestaShop 1.7 to 9. Behavior and file names may differ by version — always test changes in a staging environment before applying them in production.
Back office URL and access control
-
Rename the default /adminXXXX folder or change the admin URL when possible. Test autoloaders and module references first.
-
Restrict access by IP using the server firewall or a WAF. Use a VPN for remote teams.
-
Enforce HTTPS and HSTS; set admin cookies to Secure and HttpOnly.
Employee accounts and least privilege
-
Apply least privilege: create role-specific profiles (catalog, orders, support) and avoid using super-admin accounts for routine tasks.
-
Disable or remove inactive accounts and rotate passwords when someone leaves.
-
Enforce strong password policies and sensible rotation intervals.
Two-factor authentication (2FA)
-
Enable 2FA for all administrative accounts. Prefer TOTP apps (Google Authenticator, Authy) or FIDO2 hardware keys where available.
-
Document account recovery procedures and store recovery codes in a secure vault.
Updates and patching
-
Keep PrestaShop, the theme, PHP, MySQL and server components up to date — patches often fix security flaws.
-
Test updates in staging and automate backups before production deployments.
Module selection, auditing and removal
-
Only install modules from trusted sources: PrestaShop Addons, reputable developers or controlled repositories.
-
Audit modules: review code, required permissions, used hooks, and files created at install time.
-
Remove modules safely: disable first, export data, delete files, and inspect the database for residual tables/fields.
-
Replace or quarantine unsupported or abandoned modules.
Backups and recovery plan
-
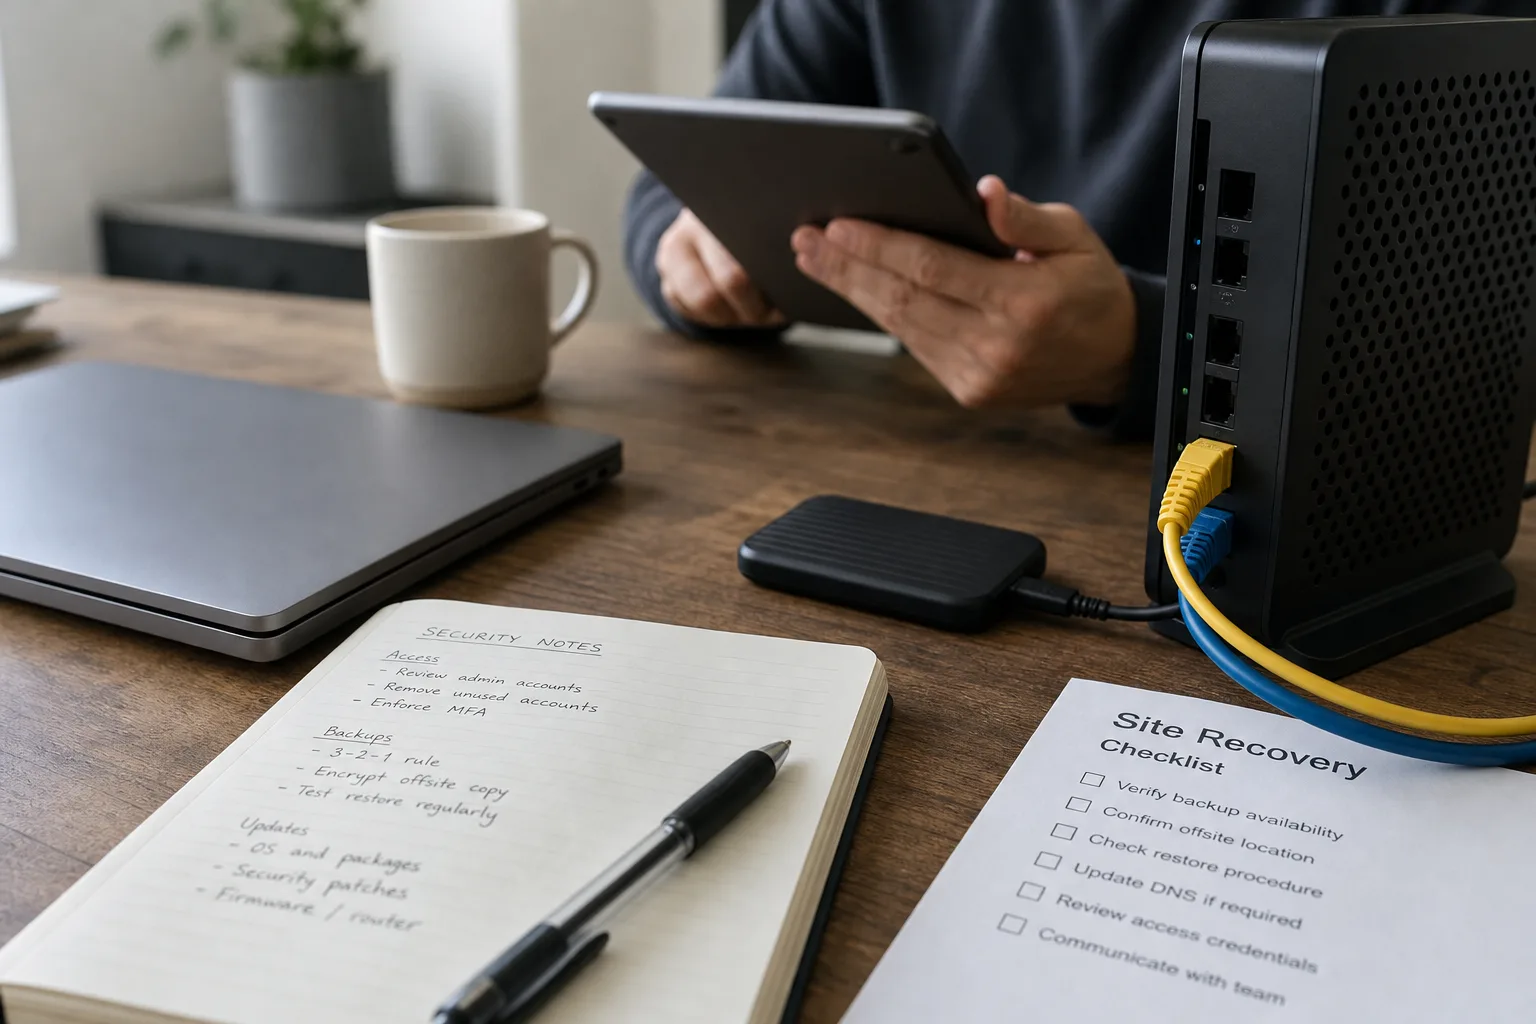
Automate regular backups of files and database. Store copies offsite and periodically test restores.
-
Keep multiple restore points (daily, weekly, monthly) depending on store activity.
Logs and anomaly detection
-
Enable and centralize logs (web server, PHP, PrestaShop where available). Protect and archive logs.
-
Monitor admin logins, module changes, file uploads and server-side file changes.
-
Create alerts for suspicious activity: repeated login failures, unexpected file changes or mass account creation.
File integrity monitoring
-
Use integrity tools (hashes/checksums) for critical files: controllers, classes, overrides and templates.
-
If a file is altered without approval, put the site into maintenance, restore from backup, and investigate.
Maintenance plan and responsibilities
-
Document a maintenance plan covering updates, testing, backups, key rotation, module audits and access reviews.
-
Assign clear roles: Dev, Ops, Support, and an escalation path to external experts when needed.
Practical checklist
-
Change admin URL and limit IP access
-
Enforce HTTPS and HSTS
-
Enable 2FA for admin accounts
-
Apply least privilege for employees
-
Keep PrestaShop and PHP updated
-
Audit and remove risky modules
-
Automate backups and test restores
-
Centralize and monitor logs
-
Monitor file integrity
-
Maintain a documented maintenance plan
Conclusion
Protecting a PrestaShop store is about layered, consistent practices: access control, cautious module management, disciplined backups and active monitoring. When in doubt or after an incident, involve specialised professionals. Securantis can help as part of a broader defensive strategy, but no single product guarantees absolute security.