

Why bots and AI-driven requests are a changing threat
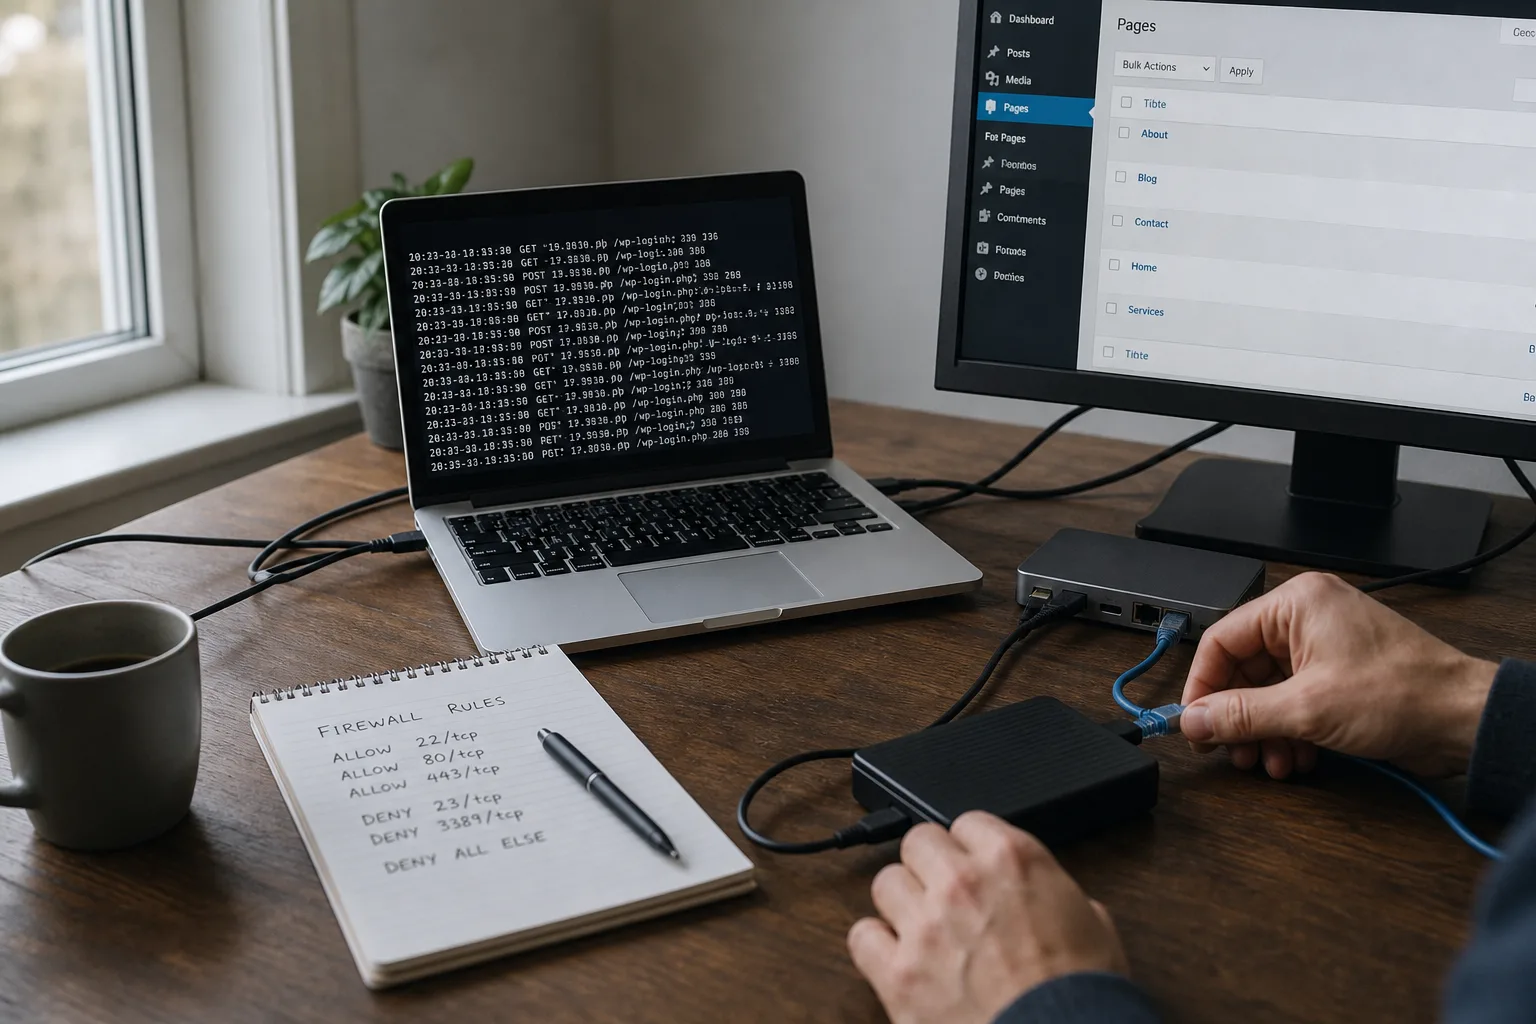
Modern AI tools combined with scraping services and botnets have made high-frequency automated requests more common. For a WordPress, WooCommerce or PrestaShop site, these flows can spike CPU usage, overload the database, saturate email queues, and enable abuse such as mass account creation or fraudulent checkouts. Effects range from degraded performance to downtime and higher hosting costs.
Rate limiting is not a silver bullet, but it is an essential defense. Properly applied, it reduces nuisance traffic, preserves capacity and makes large-scale automated abuse economically unattractive. Proper configuration must however preserve legitimate traffic like partner APIs and search engine crawlers.
Core principles of effective rate limiting
Rate limiting restricts how many requests an entity (IP, API key, session) can make in a given time window. Poorly chosen limits can block legitimate users; overly generous ones will not stop attackers. A practical solution combines network-level limits, application-specific rules per endpoint, and adaptive systems that learn normal behavior.
For e‑commerce sites it's critical to distinguish traffic types: public catalog pages, sensitive actions (add-to-cart, checkout), REST APIs, admin interfaces and webhook endpoints. Each deserves its own throttling profile.
Server-level controls: CDN, WAF and TCP throttling
Many attacks can be mitigated before they reach your CMS. A properly configured CDN blocks many bots at the edge, caches static content and offers per-path or per-country rate limits. Web Application Firewalls detect common malicious patterns and quarantine sources.
On the web server (Nginx, Apache), you can limit connections and requests per IP, enforce per-endpoint rate limits and return 429 responses for exceeding clients. Cloud providers also offer managed firewall capabilities and traffic shaping to reduce volumetric noise.
Application-level protections for forms and endpoints
Within WordPress, WooCommerce and PrestaShop, application-level controls provide useful granularity. Limit how often contact forms, account creation flows or API endpoints can be used to stop abuse of business logic. Use vetted plugins/modules but validate their compatibility and performance impact.
Protect WooCommerce endpoints for add-to-cart and checkout—these are common fraud targets. For PrestaShop, monitor webservice use and admin page access. For WordPress, isolate the REST API and disable XML‑RPC if unused.
Adaptive detection and reputation scoring
Beyond static rules, adaptive systems analyze interaction speed, action sequences and behavioral indicators. They assign a trust score to sessions and dynamically adjust throttles or require secondary checks (CAPTCHA, JS challenge).
This reduces false positives: legitimate users performing multiple valid actions typically have higher trust, while a bot hammering multiple endpoints in parallel will see its requests delayed or blocked. Integrating IP/user-agent reputation services and shared blacklists further improves effectiveness.
CAPTCHA, JS challenges and progressive friction
CAPTCHA is useful but must be applied prudently to avoid harming conversions. Use CAPTCHAs or JS challenges only for suspicious behavior. Simple JavaScript challenges (ensuring the client executes a small script) stop non‑JS bot frameworks.
Progressive friction increases difficulty for suspect clients: initially slow responses, then present a CAPTCHA, and eventually block. This preserves user experience for legitimate visitors while raising attacker costs.
APIs and third-party integrations: special handling
APIs and third-party integrations require different treatment. Use API keys, per-key quotas, and strict CORS controls. Document limits for integrators to avoid disrupting legitimate partners.
For WooCommerce and PrestaShop, enforce strong authentication for administrative APIs and apply least privilege to API keys. For webhooks, verify signatures and protect against replay attacks.
Logging, monitoring and alerting: know when to act
Rate limiting works best when combined with good visibility. Use structured logs (requests, headers, response times) and monitor key metrics—rate of 429 responses, IP churn, or latency degradation. Dashboards help tune rules and spot false positives quickly.
Keep enough evidence for forensic analysis but respect privacy and retention policies. When alert volumes are high, prioritize incidents affecting critical flows (checkout, admin API) and automate basic responses (temporary IP blocks, quarantining).
Backups, updates and least privilege
Rate limiting protects availability but does not replace other fundamentals. Maintain tested backups, apply security updates for WordPress, WooCommerce, PrestaShop and plugins, and enforce least privilege for accounts and API keys.
If an attack leads to compromise, a recent backup greatly eases recovery. If unsure how to proceed, engage a professional for incident response to preserve evidence and avoid compounding mistakes.
When to call an expert or Securantis
Persistent attacks, recurring disruptions or patterns that impact conversions justify expert help. An audit can identify weak endpoints, calibrate rate limiting and integrate adaptive controls. Securantis can advise on best practices, help implement protections and tune rules for WordPress, WooCommerce and PrestaShop while minimizing false positives.
For active incidents (sudden traffic spikes, suspected intrusion), prefer professional response to preserve evidence and limit business impact.
Practical checklist (priority actions)
-
Deploy a CDN and enable a WAF to filter traffic at the edge and reduce server load.
-
Apply per-IP and per-endpoint limits at the web server level and test thresholds gradually to avoid blocking legitimate users.
-
Protect forms and critical endpoints (checkout, login, account creation) with application-level rules, adaptive CAPTCHA and progressive friction.
-
Enable structured logging and monitor key metrics such as 429 rates and latency.
-
Require API keys and quotas for integrations, and enforce least privilege for administrative APIs.
-
Keep tested backups and apply security updates regularly.
Conclusion
Bots and AI-powered request tools represent a real operational risk for WordPress, WooCommerce and PrestaShop sites. Thoughtfully applied rate limiting, combined with peripheral defenses like CDN/WAF, adaptive detection and careful monitoring, reduces abuse while preserving legitimate user experience. Start with visibility: logs and monitoring tell you where to apply controls.
Implement perimeter filters first, then calibrate server and application rules. If configuration, tuning or active incidents exceed your capacity, engage specialists to audit and respond. This approach protects availability, reduces fraud and preserves the trust your customers place in your site.